Compliance
The Compliance page evaluates your cryptographic inventory against defined policy standards. Each standard specifies which algorithms are acceptable, which are vulnerable, and what action to take — then CBOM assesses every asset and reports violations.
Standards Library
Section titled “Standards Library”The platform ships with built-in standards and supports custom ones:
Built-in Standards
Section titled “Built-in Standards”- CNSA 2.0 — NSA Commercial National Security Algorithm Suite
- NIST PQC — Post-Quantum Cryptography transition requirements
- FIPS 140-3 — Approved algorithms and minimum key sizes
Custom Standards
Section titled “Custom Standards”Create your own organizational policies with:
- Standard name, description, and category (regulatory, industry, organizational, custom)
- Source URL (link to the reference document)
- A set of rules defining algorithm requirements
Each standard contains rules that define the status of specific algorithms:
| Field | Description |
|---|---|
| Algorithm | Algorithm name to match (e.g., RSA, AES, SHA-256) |
| Key Size | Optional key size constraint with operator (=, ≥, ≤, any) |
| Status | Classification of the algorithm |
| Deadline | Date by which migration must complete |
| Action | Required remediation (e.g., “Migrate to ML-KEM”) |
| Reason | Explanation for the classification |
Status Levels
Section titled “Status Levels”| Status | Meaning |
|---|---|
| SAFE | Quantum-resistant, no action needed |
| WEAKENED | Reduced strength post-quantum (e.g., AES-128 under Grover’s) |
| VULNERABLE | Broken by quantum, must migrate before deadline |
| COMPROMISED | Immediate action required — algorithm is already broken |
| DEPRECATED | Classically broken, must be removed everywhere |
Running Assessments
Section titled “Running Assessments”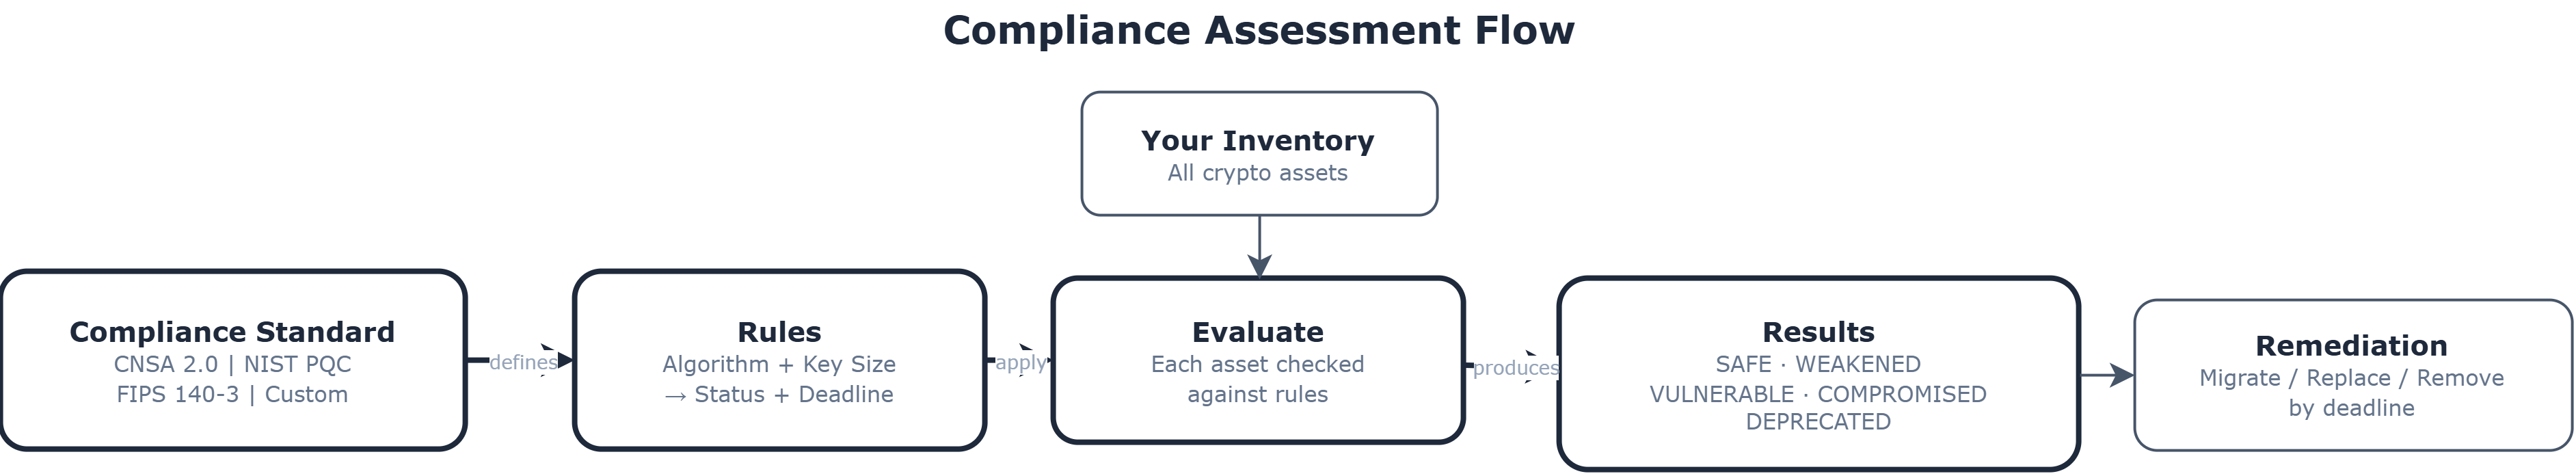
Click Run Assessment on any standard (or Run All Assessments to evaluate all at once). The assessment:
- Evaluates every asset in your inventory against the standard’s rules
- Classifies each asset’s compliance status
- Produces a detailed report with violation breakdown
Assessment Results
Section titled “Assessment Results”After running an assessment, the results view shows:
Summary
Section titled “Summary”- Total assets assessed
- Count per status: Safe, Weakened, Vulnerable, Compromised, Deprecated
- Overall status badge
- Percentage breakdown (doughnut chart)
Trend Comparison
Section titled “Trend Comparison”- Delta vs. the previous assessment for the same standard
- Direction indicator: IMPROVED, REGRESSED, or UNCHANGED
- Per-category changes (violations added/resolved)
Violations Table
Section titled “Violations Table”Tabbed by status (DEPRECATED, COMPROMISED, VULNERABLE, WEAKENED):
| Column | Description |
|---|---|
| Asset | Asset name (clickable to open detail) |
| Type | Asset type (certificate, key, etc.) |
| Algorithm | Algorithm in use |
| Key Size | Key size in bits |
| Deadline | Migration deadline from the rule |
| Action | Required action |
| Reason | Why this is a violation |
Results are paginated and searchable. Export the full assessment as JSON.
Creating a Custom Standard
Section titled “Creating a Custom Standard”- Click Create Standard
- Fill in name, category, description, and optional source URL
- Add rules — each rule specifies an algorithm, key size constraint, status, deadline, and action
- Click Save Standard
You can also Clone any existing standard (including built-ins) and modify it.
Related
Section titled “Related”- Dashboard — PQC readiness score
- Inventory — View individual assets
- Migration Planner — Plan algorithm transitions